🧠 Editorial:
Between cloud outages and sovereignty theatre
A 38-hour Microsoft outage, IT problems at the NSA, Apple and United Airlines, cyberattacks on Mittwald, and a Delos Cloud that promises digital sovereignty while Microsoft continues to supply the software.
You could be forgiven for thinking the IT industry had decided to put every buzzword around high availability, resilience and digital independence through a lengthy real-world test this week.
Spoiler alert: There’s room for improvement.
While Meta is learning that an Android permission doesn’t give it free rein, Swiss universities are showing with Nextcloud that digital alternatives can work outside a PowerPoint deck.
And ICQ just turned 30. Back then, an “Uh-oh!” was enough to tell us we had a new message. Today, apparently, we need a global status page.
Welcome to Week 47, with cloud chaos, digital sovereignty and the realisation that a working Plan B might matter more than the next AI assistant.
Enjoy the read!
📰 Tech News:
An €805 million fine for Meta: An Android permission doesn’t give apps free rein to access private photos
Meta faces an €805 million fine in Italy. The Italian data protection authority alleges that the Facebook app accesses photos and videos on Android devices without adequately informing users or obtaining their explicit consent.
The feature seems harmless at first glance.
Since 2023, Facebook has offered gallery suggestions. The app recommends photos and videos that users might want to share on Facebook. Meta says it uses only metadata for these suggestions.
The issue goes beyond how the data is processed. It comes down to consent.
In the Italian authority’s view, allowing Facebook to access photos and videos through a general Android permission does not automatically constitute consent to every feature that uses that access.
A blanket access permission is no substitute for informed consent.
That is where the authority’s decision comes in. It says the general Android permission does not tell users enough about the extent of Facebook’s access to their galleries. Gallery suggestions therefore require separate consent.
Meta now has 60 days to turn the feature off by default. It should only resume accessing the gallery for suggestions once users have explicitly opted in.
The authority is also looking at another feature that uploads gallery content to the cloud for processing. It has explicitly reserved the right to open a separate investigation.
Meta considers the fine disproportionate and intends to appeal.
The company argues that the feature simply makes it easier to share photos. It also says users can disable gallery suggestions in their privacy settings.
But being able to turn a feature off after the fact is different from explicitly agreeing to it beforehand.
The Italian authority is asking Meta to change its approach. Instead of expecting users to prevent unwanted access, it wants the company to obtain adequate consent up front.
Privacy begins with the decision to allow access in the first place.
Microsoft: 38 hours of downtime and a major dependency problem
A global Microsoft 365 outage from 12 to 14 November 2026 seriously disrupted businesses and public institutions. Exchange Online, Outlook, Teams calendars, Copilot and other services were affected in at least 74 countries.
Microsoft reported full recovery after nearly 38 hours.
The company traced the outage to an earlier network upgrade. A subsequent change set off a chain reaction that overloaded a growing number of servers. Microsoft said a cyberattack was not responsible.
Several essential services went down at the same time.
Email, calendars, communications and security tools are closely integrated within Microsoft’s ecosystem. When a central component fails, multiple business processes can grind to a halt at once.
The economic impact could also be substantial. According to the report, Anderson Economic Group put productivity losses at around US$7 billion in a preliminary estimate.
The outage highlights a structural problem: critical IT services are concentrated among a handful of providers.
In his latest MeTacheles article, Sascha Pallenberg analyses the outage and points to Schleswig-Holstein. The German state has already moved around 44,000 mailboxes from Microsoft Exchange to Open-Xchange and is expanding its use of LibreOffice and Nextcloud.
The case shows why security measures within a single platform can only go so far in building digital resilience.
Independent communication channels, alternative providers and tested emergency procedures help businesses and public authorities keep working during large-scale cloud outages.
Switching providers cannot prevent every outage. It can reduce the chance that a single technical fault will disrupt all essential business processes at once.
🔗 https://www.metacheles.de/microsoft-ausfall-die-38-stuendige-funkstille/
Delos Cloud: Microsoft is staying, and so is the dependency
Delos Cloud is due to launch for German public authorities in early 2027. The SAP subsidiary promises sovereign cloud infrastructure for federal, state and municipal bodies. Microsoft is supposed to lose direct access to the platform.
That sounds like progress. But beyond who runs the data centres, the question is who controls the technology.
Delos Cloud remains a Microsoft cloud at its core.
Microsoft will continue to supply the software and updates. Delos owns the data centres and has taken over the entire operation. Arvato Systems is involved as an operating partner.
This arrangement aims to shield government data from access by US authorities. That is an understandable goal. Legal safeguards and technological independence, however, are two different things.
Relying on one vendor for updates limits your control over your infrastructure.
The German Informatics Society’s Digital Sovereignty working group has warned about this issue. It argues that the continued reliance on Microsoft puts public institutions’ ability to act at risk.
Delos rejects the accusation of sovereignty washing.
The platform is undergoing further security assessments. It has obtained initial ISO/IEC 27001 certifications. Further C5 attestations and assessments against requirements from Germany’s Federal Office for Information Security are still pending.
These assessments matter. They document compliance with defined security requirements. The question of technological dependency remains.
Digital sovereignty goes beyond where a data centre is located.
It includes the ability to develop software independently, switch providers and operate critical systems without needing a single technology company’s permission or cooperation.
That standard is particularly important for government infrastructure.
European open-source technologies offer a foundation for this. Open standards, auditable source code and independent development can reduce structural dependencies. The open-source label alone does not make software more secure.
Delos Cloud can improve data protection and operational control. Those gains deserve recognition.
Removing Microsoft’s direct access to the servers is only one step towards cloud sovereignty.
As long as key software components and their development depend on Microsoft, a significant share of technological control will remain outside Germany.
That should not be the long-term goal for public administration.
NSA, Apple and United Airlines: A series of IT outages gives pause
Several major organisations experienced serious IT disruption on Tuesday, including the US National Security Agency, Apple and United Airlines.
The NSA outage was especially notable.
The US intelligence agency’s internal communications network, which also carries classified information, was temporarily unavailable.
The NSA confirmed technical problems related to scheduled maintenance. Its Maryland headquarters declared “Code Yellow,” and some staff were asked to report to work at staggered times.
The agency said it remained able to carry out its core work. The White House said there was no evidence of a cyberattack.
Apple also faced widespread disruption.
The outages affected iCloud, iCloud Mail, Apple Business and several education services. Developer platforms including App Store Connect and the Developer ID Notary Service were also temporarily unavailable.
It was initially unclear whether Apple’s outages had a common cause.
At United Airlines, an outage lasting about an hour prevented aircraft from being processed. Passengers had to wait, and some had to leave planes they had already boarded.
The incidents follow other technical disruptions in US aviation and banking, as well as last week’s roughly 38-hour Microsoft outage.
The cluster of outages is striking. There is no evidence of a common technical cause.
It would be premature to link the incidents.
They do show that major technology companies, critical infrastructure and security agencies can all experience serious system outages.
Reliable communications and IT systems are particularly important for organisations like the NSA and for aviation.
The practical response is to review failover, redundancy and emergency procedures systematically.
Technical failures cannot be eliminated entirely. Their impact needs to remain manageable.
30 years of ICQ: When a number was all you needed to stay in touch
“Uh-oh!” If you spent time online in the late 1990s or early 2000s, you probably recognise that notification sound immediately.
ICQ launched on 15 November 1996 and would just have celebrated its 30th birthday. For a generation, it was one of their first formative experiences with online communication.
The Israeli start-up Mirabilis developed ICQ, which stood for “I seek you.” The idea was simple: you could send messages, manage contacts and talk to people even if you were not both online at the same time.
That is standard on WhatsApp and other messengers today. ICQ made it popular in the 1990s.
An ICQ number was once almost as important as a phone number.
For gamers and internet enthusiasts in particular, their personal identification number, or UIN, was an essential contact detail. Many knew it by heart.
ICQ started automatically on many Windows computers. Your contact list told you who was available. Away from home, you could sign in with your number on someone else’s computer or at an internet café.
The service took off quickly. In 1998, AOL acquired the company for US$287 million, with up to US$120 million more in performance-related payments. At the time, ICQ had around 12 million users.
By 2009 there were more than 470 million registered accounts, although that figure did not represent individual users.
Then smartphones changed the market.
As mobile messengers such as WhatsApp spread, ICQ became less relevant. A 2020 relaunch under the name “ICQ New” could not reverse the decline.
The service shut down on 26 June 2024.
ICQ hasn’t disappeared entirely. Since August 2026, the fan project ICQ Reborn has been trying to bring it back. The project reportedly has around 2,000 users. Original ICQ numbers no longer work.
ICQ remains a remarkable chapter in internet history.
It established communication habits we now take for granted. It also recalls an era when being reachable online was far more closely tied to the computer at home.
A personal number and a distinctive “Uh-oh!” were enough to connect millions of people.
Who still remembers their old ICQ number by heart?
Cyberattack on Mittwald: A second attack disrupts administration services again
German web host Mittwald is dealing with the fallout from several cyberattacks. An initial attack on 5 November came through the company’s own Model Context Protocol (MCP) server. Another attack overnight into 12 November caused significant disruption again.
Key administration services were affected. The customer centre, the mStudio administration interface and SSH access were temporarily unavailable. The ordering system and Mittwald Extensions also faced restrictions.
After a gradual restoration through 7 November, the second attack led to further outages.
The company’s own website is also operating in emergency mode.
Mittwald took its regular site offline as a precaution and replaced it with a status page. Many pages, including its blog and information about the incident, were no longer accessible.
The company expressly denies reports that attackers may have tampered with the website. It told heise security that the attackers had neither taken over nor defaced the site.
Customer websites reportedly remain accessible.
According to Mittwald, the shutdowns did not affect hosted customer sites, which remained accessible throughout. The restrictions mainly affected administration infrastructure and internal services.
Mittwald described the attackers as professionals who appear to use AI assistance. The company plans to publish technical details about the attacks and its response once the work is complete.
The incident draws attention to MCP security.
The Model Context Protocol lets AI applications connect to external systems and services. These integrations expand what applications can do and create additional points of access that infrastructure teams need to secure.
The report does not identify the specific vulnerability the attackers exploited or the extent of the compromise.
The case shows that an incident at a hosting provider does not necessarily take customer websites offline. Losing access to central administration services can still make day-to-day operations considerably harder.
📰 Short News:
1. US tightens export controls on chips
The US is introducing a licensing requirement for chip exports, increasing its influence over international technology supply chains. Companies that rely on US semiconductors and AI hardware are especially exposed. For Europe, it is another reminder that a lack of control over key technologies leaves it dependent on political decisions in Washington.
2. BundID faces a wave of unauthorised login attempts
Germany’s government-run BundID citizen account service was targeted by large numbers of unauthorised login attempts. The incident underlines how security-critical central digital identity systems are. As more public services move online, attack detection, resilience and transparent security processes matter even more. Digital government needs reliable security architecture as well as working platforms.
3. Germany’s BSI warns of serious firmware vulnerabilities in cooling systems
Serious firmware vulnerabilities continue to put networked cooling systems at risk. Germany’s Federal Office for Information Security (BSI) is warning of risks that extend well beyond conventional IT. Insecure industrial controls can disrupt operations and critical supply processes. Mandatory security standards, long-term firmware updates and auditable supply chains are essential to Europe’s digital resilience.
💡 Good News:
Swiss universities switch to Nextcloud
The Swiss foundation Switch is migrating its cloud storage service, Switch Drive, from ownCloud to Nextcloud, the open-source platform from Germany. The migration covers 65 higher education institutions, around 39,500 users and 585 terabytes of data.
Support for the existing platform was coming to an end. By choosing Nextcloud, Switch is sticking with open source and aims to improve performance, security and digital sovereignty.
The migration took place over a weekend with minimal disruption. Switch says users reported significantly better performance afterwards.
🔗 https://www.inside-it.ch/switch-migriert-hochschulen-auf-nextcloud-20261116
🎧 Podcast recommendation:
Digital sovereignty works when you follow through
A year without US cloud services. In the latest episode of MeTacheles Tonspur, Sascha Pallenberg reflects on his decision to move away from Big Tech.
After 25 years of covering Silicon Valley, he has overhauled most of his digital setup: Proton for email, IONOS and Nextcloud for cloud services, Linux for his operating system and PeerTube for video.
His conclusion is that European and open alternatives are already more practical than they often get credit for.
He also looks at sovereignty washing. Choosing a European provider alone cannot guarantee digital independence when US companies still control the underlying technology.
Pallenberg also reports on 14 events in Germany, Austria and Switzerland. He sees growing interest in digital alternatives. Initiatives in Schleswig-Holstein, Thuringia and Bavaria, along with developments in France and the Netherlands, point to movement at the policy level too.
His forecast is ambitious: by the end of 2027, better alternatives could be available for every use case.
It’s a personal account worth listening to, with concrete examples, a clear point of view and an optimistic take on what Europe can do with technology.
🎧 MeTacheles Tonspur – Sascha Pallenberg
☸️ Kubernetes Updates:
Kubernetes is retiring IPVS: Removal planned for version 1.40
Kubernetes has announced a significant change to its networking architecture. The kube-proxy IPVS backend is scheduled for complete removal in version 1.40. It has been deprecated since Kubernetes 1.35.
IPVS was originally introduced to address iptables performance issues. Large clusters in particular benefited from better scalability.
However, the Linux IPVS interface turned out to be incompatible with some Kubernetes Services API requirements. The need for additional iptables rules, functional limitations and high maintenance costs eventually led the project to retire IPVS.
nftables is the recommended alternative.
The backend has been stable since Kubernetes 1.33. The project says it delivers at least comparable performance and supports all Service features.
For clusters running Kubernetes 1.36 or later on Linux kernel 5.13 or later, the project recommends moving to nftables. iptables remains an option and has seen considerable performance improvements in recent years.
Kubernetes cluster operators should start preparing now.
Review existing IPVS configurations and plan the migration ahead of time. Moving to nftables generally requires changing the kube-proxy configuration and restarting the relevant pods.
The change reduces technical complexity and gives Kubernetes a more maintainable networking stack over the long term.
🔗 https://kubernetes.io/blog/2026/11/16/ipvs-removal/
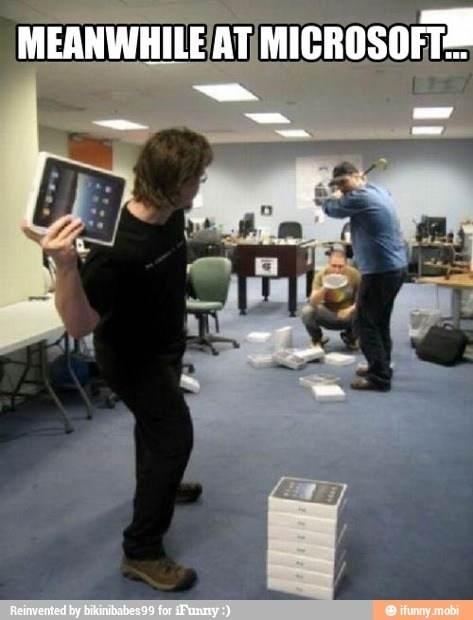
😄 Meme of the Week: